
Modernising legacy contracts for a new era of third-party risk
Ahead of Vendor & Third Party Risk Europe, we spoke with Michal Drohomirecki, Head of Information and Cybersecurity Contract Support - Third Party Security Risk at Standard Chartered Bank, who gave us an exclusive teaser of what to expect from his session on contract remediation under regulatory pressure.
Where do legacy contracts most commonly fail to meet new regulatory
requirements?
Legacy contracts most often fail because regulation moves faster than
contract design and organisational change. Typical gaps include:
- Privacy & ICT regulation lag – contracts predate GDPR evolution, NIS2 and DORA, lacking enforceable data, cyber, and resilience obligations.
- Modern risk blind spots – limited expertise when contracts were signed means cyber, operational resilience, and ICT concentration risks are not properly addressed.
- Sub-contracting & nth party risk – weak controls over subcontractors and fourth parties, with no transparency or regulatory flow down.
- Exit rights misaligned to regulation – termination focused on commercial breach only, not regulatory non-compliance or cyber security failures.
- Cyber, privacy and regulatory standards evolve faster than uptake – security clauses are static while threats and expectations change, exposing slow organisational adaptation.
Bottom line: legacy contracts reflect yesterday’s risk model, while
regulation assumes dynamic, end to end control over today’s digital and third
party ecosystem.
What
does vendor pushback typically look like, and how is it overcome?
Pushback
typically looks like…
- Pushback on sub‑contractor transparency (nth‑party disclosure)
- Reluctance to accept non‑commercial exit rights (e.g. for regulatory or cyber non‑compliance)
- Claims that new controls are costly, operationally heavy, or unnecessary
How it’s overcome:
- Reframing requirements as regulatory obligations, not negotiable asks
- Using risk‑based proportionality (apply stricter clauses only to critical services)
- Compensating controls mitigate clause gaps – where full contractual alignment is resisted, firms document alternative controls (e.g. independent assurance, continuous monitoring, internal oversight, segregated access, escalation rights) that demonstrate equivalent protection, instead of removing the clause entirely or accepting unmanaged risk.
Pushback is commercial by default; it is resolved when compliance is
positioned as a regulatory necessity and condition of doing business, not a
preference.
How
do organisations standardise remediation across large contract portfolios?
- Prioritise by risk and materiality – focus first on critical services, high‑risk vendors, and regulatory impact.
- Use trigger points – remediation embedded into renewals, amendments, extensions, or onboarding rather than stand‑alone re‑papering.
- Dedicated ownership model – clearly defined teams with authority over contract negotiation, risk acceptance, and risk register updates. These teams not only explain risk to the business, but identify compensating controls, approve amendments, and formally accept residual risk.
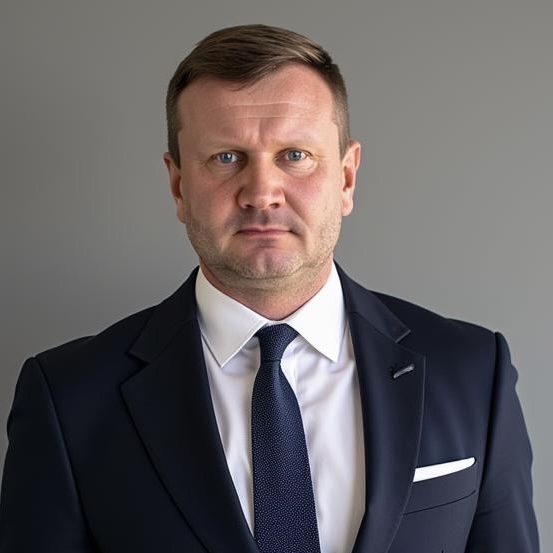
Michal Drohomirecki
Head of ICS Contract Support, Standard Chartered
Michal Drohomirecki is an information security and supply chain risk specialist with over 15 years of experience in vendor management and risk oversight, including more than 6 years focused specifically on cybersecurity risk. He specializes in third-party risk assessments, supplier security audits, defining security requirements, and drafting contractual security clauses. Michal supports organizations in designing and strengthening third-party risk management (TPRM) processes, aligning them with evolving regulatory and industry frameworks.
LinkedIn profile