
AI Can't Save You: Why Third-Party Risk Still Rests on Human Judgement
display-middle-ads-here
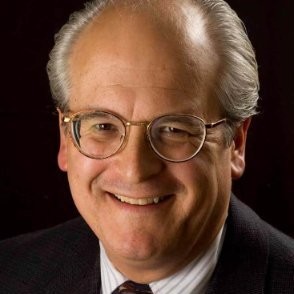
On Operational Risk and Resilience: Q&A Interview with Phil Gledhill, Supervising Examiner, Federal Reserve Bank of New York
Disclaimer: The views expressed below are Phil Gledhill’s and do not reflect the views of the Federal Reserve Bank of New York or the Federal Reserve System.
There’s a lot of talk around emerging tech – AI, blockchain, automation. Which of these do you think will actually move the needle in third-party risk, and how?
All of these technologies will have an impact on the way services are provided. The speed with which technology is advancing is unprecedented, and financial institutions need to be ahead of the curve in understanding these new technologies and preparing to mitigate the risks that they pose. The good news is that industry leaders have the opportunity to design solid risk management frameworks and systems to help prevent damage to a firm before a risk manifests or detect damage before the risk spirals out of control.
Firms that deploy third parties to provide services to customers and support their internal operations can look to reliable, long-standing principles to establish frameworks that manage both existing and emerging technology risks.
Overarching principles such as active board and senior management oversight, clear policies and operating procedures, effective communication of management information throughout the firm, and effective internal controls should be fully embedded in the firm’s risk DNA before considering emerging technologies since these principles will form the backbone of a third-party risk program.
As risks continue to evolve, how can institutions stay agile without constantly overhauling their TPRM frameworks? Is it about mindset, tools, or something else?
Over the past 25 years, technology risks have evolved
dramatically, along with firms’ exponential growth in using third parties to
provide services to customers and support internal operations.
What has remained constant are the core principles that provide safety and soundness to a firm’s operation, and indeed the financial system. For example, the basic principle concerning risk ownership (whereby the firm retains the risk of an outsourced operation) has not changed.
Defining a clear strategy and risk appetite for third-party activities, effective risk assessment of services being outsourced, the application of controls at the vendor, and an honest assessment of the firm’s current capabilities in tools, staff expertise, and resources to manage the level of risk posed by emerging technologies… none of these principles have changed.[2] We can be confident that these tenets will provide effective support to an institution as it navigates risk.
What’s the potential for more collaboration across the industry – do you think there’s an appetite for more shared approaches or even shared infrastructure in third-party risk?
I think there is tremendous potential for more collaborative learning in this space. And while the risk appetite to engage new third parties will continue to vary from firm to firm, what matters most is that leaders manage innovation responsibly.
Much of the work performed
within a robust third-party framework is duplicative both internally and
externally at other firms. Vendors traditionally have been spending a great
deal of time providing customized reports, assessments of internal controls,
testing recovery plans[3],
and so on for multiple clients.
Defining ways to streamline all of this, for both the firm and the vendor, is useful. Firms should continue to update their approaches based on current guidance and principles as infrastructure changes will adjust the level of risk, which must be continually re-assessed. Some will shy away from collaborative approaches whereas others will embrace them.
As a reminder, having a fully functional third-party framework that’s wholly embedded in the firm’s broader risk management framework is the best defense against risk.
How do you see the role of supervision evolving in this space – do you expect there will be more prescriptive guidance or a continued push for firms to define their own risk appetites and frameworks?
Each firm is unique, with its own business strategies, risk appetites, customers, and business environments. Regardless of whether interagency guidance becomes more prescriptive, the current guidance (e.g. SR letters 95-51, SR 20-2,4 and SR 23-04) is broadly applicable and principles-based, allowing firms to create frameworks that specifically manage their idiosyncratic risks while providing room for risk-managed innovation.
If we’re looking ahead to 2030, what do you see as the most important principles and priorities that the industry should be attuned to when it comes to third-party risk management?
Considering the leaps made over the past few years, it’s hard to imagine the technology landscape beyond 2026, let alone in 2030. There’s no doubt that the landscape will evolve, and management needs to keep pace with that. Yet third-party risk management frameworks, when established and aligned with the safety and soundness principles[4] outlined in the guidance we’ve been discussing, will likely endure.
Programs with clear business and outsourcing strategies, solid assessments of risks and controls, and well-defined policies and procedures will provide the best defense against operational, financial and reputational harm, regardless of where and how an emerging technology is deployed.
[1] SR 95-51
[2] SR 23-04 (Third-Party Risk Management). This is the most current
interagency Third-Party guidance published jointly by the FRB, OCC and FDIC.
The current principles and frameworks for managing third-party risk can be
found here.
[3] SR 20-24 (Resiliency). Practitioners should be mindful of the
interlocking principles between this guidance and the principles noted in SR
23-04.
[4] SR 95-51, SR 20-24, and SR 23-04.