The rise of fourth-party risks and global regulations like DORA are reshaping Third Party Risk Management (TPRM). Hilda Andeliz emphasizes that proactivity, leadership engagement, and adaptability are critical for managing increasingly complex and interco
display-middle-ads-here
No one can argue that a world that’s shrinking in terms of communication and logistics is in many ways easier to do business in. But that interconnectedness comes at a price, especially when that world is also a hostage to increasing volatility.
One area that has become thorny for the global financial services sector is Third Party Risk Management.
But in fact, even that doesn’t really do justice to the scale of the challenges that risk management leaders face in ensuring their TPRM strategies are mature and resilient, because the reach of TPRM is moving rapidly into the onion skin-like conundrum that is nth party management.
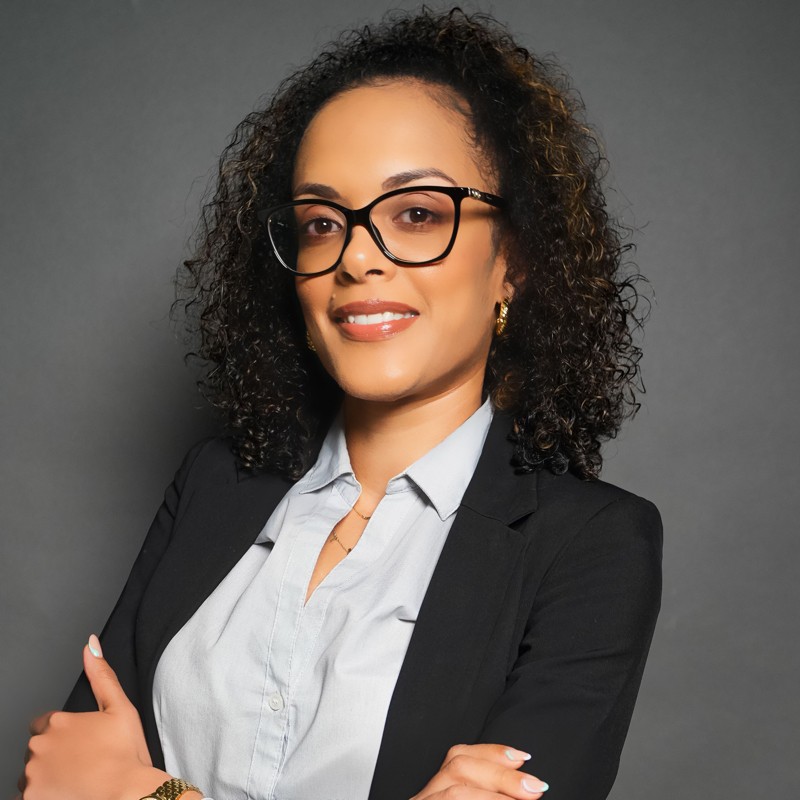
In a recent CeFPro webinar dedicated to TPRM resilience, Hilda Andeliz, a performance analyst at Raleigh Bank, hared her journey and insights, shedding light on the complexities of TPRM and the evolving challenges faced by organizations today.
Andeliz began her career in retail banking, a sector she fondly refers to as "the heart of the industry." She held various roles, from branch and business center positions to assistant manager and loss prevention advisor.
Two years ago, she transitioned into TPRM—a move she describes as stepping into “unknown waters.” The move couldn’t have come at a more interesting time in the evolution of third-party risk management.
One of the key topics discussed during the panel was the overconfidence organizations often exhibit regarding their TPRM programs.
According to Andeliz, this overconfidence stems from having a structured system without fully understanding its resilience under regulatory scrutiny. “Many organizations will say they have a centralized and integrated team,” she explained. “But when it comes to defending, the real challenge is showing that they actually are working in practice.”
She emphasized the importance of moving beyond superficial frameworks. “Defending the TPRM program,” she says, “is more than having a nice framework. It requires ongoing oversight, up-to-date data, and, of course, senior leadership engagement.”
With the growing influence of international regulations, such as Europe’s Digital Operational Resilience Act (DORA), and their potential impact on U.S. practices, the issue of how far regulatory change is a driver for action inevitably found itself in the spotlight, too.
“We are going to learn a lot from DORA and how Europe handles it,” Andeliz admitted. In looking at how the US might respond to the European experience, she identified the need for C-suite involvement.
“That’s the key to everything,” she said. “If leaders are involved and informed, it gives the vendor management team the tools and resources they need.”